
Tumbleweed Monthly Update - September 2026
There were several software package updates for openSUSE Tumbleweed during the month of September and with openSUSE.Asia Summit 2026 about to begin, we are bringing the monthly review to you early.
September delivered a stacked month of snapshots across the desktop, developer tooling, and security surface. KDE Plasma 6.7.5 landed with fixes for KWin display management and taskbar refinements, while KDE Frameworks 6.30.0 and KDE Gear 26.08.1 delivered new features and bugfixes across the KDE ecosystem. glibc jumped to 2.44 with Transparent Huge Pages tunables and optimized math functions, and LLVM 23.1.1 arrived with important bugfixes. Mesa progressed from 26.2.2 to 26.2.3 and the Linux kernel advanced through 7.2.5 to 7.2.7 with a sustained focus on security. Later in the month the GNOME desktop picked up 50.5 across gnome-shell and mutter, GIMP advanced to 3.2.6, coreutils jumped to 9.12, and rsync arrived at 3.5.1 after a sweeping audit of its path handling and daemon protocol. curl addressed seven CVEs, pcre2 patched six security issues, and ffmpeg rolled up more than 20 CVEs in one pass.
As always, be sure to roll back using snapper if any issues arise.
For more details on the change logs for the month, visit the openSUSE Factory mailing list.
New Features and Enhancements
KDE Plasma 6.7.5: The fifth bugfix release of the Plasma 6.7 series brings targeted refinements across the desktop. KWin fixes the global removal timer timeout for unplugged outputs, and Discover resolves update stalling when fwupd is unavailable and a regression where updates were mistaken for needing a reboot. Spectacle fixes a crash during window-under-pointer detection and annotation submenu overflow, while the taskbar applet corrects right-to-left layout rendering and prevents duplicate favorites launching on Space.
KDE Frameworks 6.30.0: A feature release of the KDE component libraries that arrives with refinements across KIO, Kirigami, and KTextEditor. KIO fixes FTP command case consistency, corrects folder size reporting to include filesystem overhead, and lets a folder with the setgid bit propagate its group to copied files. KTextEditor gains vi-mode filename registers and fixes block operations with tabs. Baloo now excludes .snapshots folders from indexing, KCalendarCore adds recurrenceDescription and translated enum names, and KCodecs improves encoding detection with better confidence scoring. Syntax Highlighting adds DotEnv, KDL, and Just language support, and KGuiAddons adds a geo: URI handler for Cartes.
KDE Gear 26.08.1: The first bugfix release of the 26.08 series arrives with targeted fixes across the KDE application collection. Dolphin fixes the active split pane not being set correctly, corrects default zoom level calculations based on preview state, and prevents zero icon sizes in item layouts. Okular fixes a crash on broken DVI files, addresses dangling form field pointers after saving, and backports a Synctex security fix. Konsole corrects OSC22 mouse cursor shapes for splits and fixes focus shortcut issues in ViewSplitter. Kitinerary adds parsers for Air Canada and Lufthansa PDF itineraries and optimizes Wikidata train station queries. KOrganizer fixes search dialog functionality after editing a result.
GNOME Shell & mutter 50.5: The GNOME desktop received quality-of-life fixes that clean up day-to-day use. The unlock dialog handles keyboard navigation correctly, the screen will no longer unlock once a screen time limit has been reached, and toggling the wireless switch no longer blocks. On the compositor side, mutter fixes a hang on external monitor hotplug, stops multiple monitors from all being reported as primary, corrects desaturated SDR content in HDR mode, and adds per-view control over the software cursor overlay. libadwaita 1.9.4 arrived alongside with annotation and idle-callback fixes in AdwAnimation, AdwActionRow, AdwTabBar and AdwTabGrid, and GNOME Maps 50.5 fixed the secondary icons shown for recent and favorite places in initial search results.
GIMP 3.2.6: The image editor continued its 3.2 series with a large batch of fixes and some preparation for a future GTK 4 port. The Heal tool no longer leaves a dark smudge at crop boundaries, the Crop tool keeps vector layers in place, and the Color Picker correctly honours the Sample Merged option on single-layer images. Layer groups with non-destructive filters no longer get an unwanted pass-through reduction, plug-in pipes and process watching are better managed on exit so fewer warnings appear when closing GIMP, and clipboard brush and pattern sizes are raised to 8192 on AArch64. The XCF format is bumped to version 26 to record path visibility locks and channel filters.
Shotwell 33.0: The GNOME photo manager completed its port to GTK 4, moving to version 33 after the long-running 0.32 series. Printing was reworked, the publishing targets gained a “peek password” icon and now use a simple localhost web server instead of a dedicated authentication helper, and toast notifications replace many of the simpler dialogs. Face detection and recognition see a long list of fixes around names, highlighting and random matching, and the viewer mode now shows system information and can be opened for arbitrary URIs.
glibc 2.44: A major version bump that brings system-wide tunables via /etc/tunables.conf and a new glibc.elf.thp tunable that maps read-only segments with Transparent Huge Pages when the kernel has not disabled THP. The malloc page size is now capped to MAX_THP_PAGESIZE, and the CORE-MATH project contributions bring additional optimized and correctly rounded math functions. On AArch64, log, exp, sin, cas, sinh, cosh, and other special cases are vectorized for SVE and AdvSIMD, while RISC-V gains vector extension optimized variants of memcmp, memcpy, strcmp, strlen, and more. The release also carries two security fixes for stack-based buffer clashing during tilde expansion in wordexp (CVE-2026-6791) and an invalid free() call with WRDE_APPEND (CVE-2026-6368).
LibreOffice 26.8.0.3: A major version bump from the 26.2 series that brings updated bundled pdfium to 7681 and Skia to m147 as required by the new download configuration. The release drops Qt 5 support in Tumbleweed in favor of Qt 6, aligning with the broader KDE ecosystem move away from Qt 5. Users of the office suite will see improved compatibility and performance across Writer, Calc, and Impress.
LLVM 23.1.1: A bugfix release for the LLVM 23.1.0 series that addresses issues found since the initial release. The update is API and ABI compatible with 23.1.0, making it a safe upgrade for developers who depend on the Clang compiler, LLVM libraries, and related tooling. This is particularly relevant for users building packages that depend on the LLVM infrastructure for compilation.
harfbuzz 14.4.0 & 14.5.0: The text shaping engine that underpins rendering in browsers, desktop environments, and document editors received important improvements. In 14.4.0, glyph positions and extents now saturate instead of overflowing, Arabic Windows-1256 fallback shaping is enabled on all platforms, the COLR sweep gradient truncation and unbounded memory use are fixed, and subsetting is faster especially for large GSUB/GPOS and CFF tables. Version 14.5.0 then updated the Unicode data to 18.0, adding script values for Jurchen, Proto-Cuneiform and Seal along with the matching shaping support, and introduced rendering work budgets shared across the raster, vector, GPU and Cairo renderers so nested outline work stays bounded. The DirectWrite backend no longer uses the C++ runtime, and the HarfRust integration shaper sees various improvements.
bubblewrap 0.12.0: The Linux sandboxing tool removes support for building a setuid binary, as all modern distributions now support unprivileged user namespaces. A security fix resolves a symlink issue where a file or directory creation during sandbox setup could follow parent symlinks out of the sandbox. The --not-a-security-boundary flag is added for cases where some sandbox setup failures should not be fatal.
Key Package Updates
Linux kernel 7.2.2 through 7.2.7: The kernel progressed through six point releases during September with a sustained focus on security and stability. Version 7.2.2 carried fixes for ptp vmclock read-only mapping vulnerability and GSO state stripping from fragments before forwarding . Version 7.2.3 addressed an extensive list of USB fixes including use-after-free in usbdev_release(), ALSA USB audio out-of-bounds write in snd_usbmidi_novation_output(), and KVM SEV improvements for SNP guests. Version 7.2.4 added fixes for dm-pcache use-after-free, wifi driver memory leaks across mt76, iwlwifi, and brcmfmac, and I3C device master use-after-free in the unregister path. Version 7.2.5 was dominated by backports, among them a large sweep of NFC fixes bounding device-reported lengths, rejecting undersized LLCP PDUs, and fixing an out-of-bounds write in nci_target_active, alongside futex priority-inheritance races and io_uring iovec leaks. Version 7.2.6 brought an exceptionally long list of nfsd hardening patches covering use-after-free in the fcache disposal path, layout_fence_worker double references, and nfsd_file leaks on inter-server COPY, plus a clocksource IRQ leak fix and an iomap integrity-payload fix. Version 7.2.7 wrapped up the month with a broad set covering Btrfs write-protection during data writeback, AppArmor credential use-after-free and a null-termination out-of-bounds write, mm and MGLRU correctness, and a large group of tracing use-after-free and crash fixes.
Mesa 26.2.2 & 26.2.3: Two bugfix releases landed on the 26.2 branch. Alongside the usual stream of regression fixes, openSUSE’s build gained the rocket Gallium driver for Rockchip NPUs on aarch64, and the new Mesa-teflon-delegate subpackage ships a TensorFlow Lite delegate for NPUs. The changelogs point to the Mesa 26.2.2 and Mesa 26.2.3 release notes for details, and the LLVM 23 build fix that unblocked both releases came along with them. Users on AMD, Intel, or Qualcomm hardware who experienced rendering issues after earlier Mesa updates should find these releases more stable.
rsync 3.5.1: The file synchronization tool received a sweeping security overhaul. A focused audit of path handling and the daemon protocol, a companion fuzzing pass and external reports produced 33 fixes covering restricted-directory escapes in rrsync, daemon module-root chdir escapes under use chroot = no, --relative implied-parent creation escaping the destination tree, daemon --filter merge file bypasses, and a range of symlink races on the sender and receiver sides. The release also fixes an unauthenticated TLS connection in rsync-ssl and a hosts deny rule that failed open when a configured hostname could not be resolved. A 3.5.1 follow-up in the same snapshot fixed several path-handling regressions from 3.5.0, restored access to /dev/stdin and friends inside user namespaces, tightened partial-directory validation on the receiver, added support for internationalised domain names, and bumped the protocol number to 33.
util-linux 2.42.3: The Linux utility suite received a security-focused point release. Four mount(8) and namespace-related CVEs are fixed, including post-mount hooks running after an external mount helper fails and a time-of-check/time-of-use race on the source path in restricted SUID mode. wall and write gained an additional fix for terminal escape sequence injection through the banner hostname, complementing the earlier CVE-2024-28085 work. Alongside the security work, the release fixes an out-of-bounds read of the ISO9660 root directory record in libblkid, an out-of-bounds write in get_line() on invalid multibyte input, and a pg out-of-bounds access on a trailing tab.
PipeWire 1.6.9: The sound and video server shipped a bugfix release that is API and ABI compatible with the rest of the 1.6 series. RAOP (AirPlay) support sees the most work, with encryption fixed for OpenSSL 3 and above, truncated audio and metadata update problems resolved, and RAOP over TCP fixed. The resampler cutoff frequencies were tweaked to preserve more high frequencies when upsampling, potential overflows in client node buffer checks were fixed, and pw-cat now handles EOF correctly for encoded files while pw-record supports A-law.
poppler 26.09.0: The PDF rendering library jumped two minor releases, picking up 26.08.0 on the way. Fonts are now subset when saving changes in annotations and forms through fontconfig, which required making harfbuzz a build dependency. pdftotext gains a -urls option to print link URLs next to their text, pdftohtml no longer crashes when using data URLs and skips tiling patterns earlier for speed, and pdfimages gains min-height and min-width options. The core also stops infinite looping on a wrong NSS password and fixes crashes on malformed documents.
BlueZ 5.87: The Bluetooth stack jumped five releases from 5.82, bringing LE Audio and profile work along with it. Version 5.83 added AVDTP TX timestamps and fixed handling of BAP PAC removal, broadcast receiver SIDs, and HID service records; 5.84 added unicast endpoint reconfiguration, encrypted broadcast sources and HFP Caller Line Identification; 5.85 added HFP call answer and simple 3-way call support and corrected battery charge level display; 5.86 added the Telephony, Ranging, GMAP and TMAP profiles and fixed the G.722 16 kHz codec ID; and 5.87 resolved a long list of BAP, BASS, PBAP, MCP, AVRCP and GATT database issues.
cryptsetup 2.8.8: The disk encryption tool received a feature and hardening release. integritysetup gained support for keyed discards via a new --allow-discards-keyed option, which permanently upgrades the superblock so that an integrity device in standalone mode with a keyed integrity algorithm can no longer have part of itself wiped with a discard pattern. The library also closes a time-of-check/time-of-use issue in LUKS header restore by opening the device only once, which affects both LUKS1 and LUKS2, hardens BITLK metadata validation against a wrong key buffer size and a deliberate infinite loop, and fixes a possible integer overflow in the anti-forensic data size calculation on 32-bit systems.
gzip 1.15: The ubiquitous compression utility reached a new major version, landing fixes for two earlier security issues and a batch of long-standing bugs. A buffer overflow when decompressing an .lzh file after a .Z file is fixed, as is a use of uninitialized memory on some malformed inputs. gzip -d no longer rejects PKZIP signatures and local headers that legitimately appear in well-formed streamed zip files, diagnostics now quote file names containing unusual characters, and gzip --synchronous works again on platforms with O_PATH. Behaviorally, gzip follows the locale from the environment instead of insisting on the C locale, and -l reports -Inf% rather than 0.0% for an empty file.
libinput 1.32: The input handling library arrived with input-device improvements. Circular scrolling now works on circular touchpads such as the Panasonic CF-SV1, dragging on a touchpad automatically enables a drag lock when a finger nears the edge, and disable-while-typing no longer cancels an interaction already in progress. Tablets can now map the physical eraser button to any button, and libinput record accepts a --no-events flag.
lightdm 1.33.1: The display manager received a bugfix release with a notable feature. A Qt6 client library is now shipped alongside the Qt5 one, and the release fixes user switching after logind dropped the CanMultiSession property. Wayland sessions are now allowed on seat0 without VTs, PAM modules that change the home directory are handled correctly, the VNC server command is honored with IPv6 tried first for the bind, a local X server is not reused when the hostname has changed, and memory leaks in session_child_run are plugged.
AppStream 1.2.0: The software metadata standard reached a new major version and marks the libappstream-compose API as stable. appstream-compose gains an out-of-process media worker with a basic Landlock-based sandbox, switches image processing from GdkPixbuf to VIPS, and makes JPEG XL the default output format. New <heading> markup is supported in AppStream descriptions, and the news tools gain inline Markdown support along with header handling across the XML, YAML and Markdown conversions.
xz 5.8.4: The compression library received a bugfix release that includes a security fix. An invalid memory access in lzma_alone_decoder(), lzma_lzip_decoder(), lzma_auto_decoder() and lzma_microlzma_decoder() after a failed allocation is followed by decoder reinitialization is fixed, along with two use-after-free bugs in xz itself via --files/--files0 and --verbose with redirected stderr. Landlock ABI 9 support is added, a performance issue and theoretical integer overflow in lzma_index_cat() are fixed, and xz --list no longer overflows its totals.
VirtualBox 7.2.18: The VirtualBox hypervisor received a bugfix release. Data corruption in VDI differencing images after writing full blocks of zeroes and reopening the image is fixed, a VM process crash on Linux hosts with 3D acceleration enabled is resolved, and the shared clipboard no longer strips the first character from a file name located directly in a filesystem root. Linux 7.3-rc support is added.
libgcrypt 1.12.4: The GnuPG cryptographic library received a follow-up point release. RSA PSS handling of very large salt lengths is fixed, the length of hashed input is validated for RSA PSS, and the RSA OAEP decoder validates all-zero padding for correctness. Padding in cSHAKE was corrected against NIST ACVP conformance vectors, and a build problem with some compiler versions around SM4 instructions is resolved.
GStreamer 1.28.7: A wide-ranging update across the core and plugin packages with both security and playback fixes. The appsrc element fixes a regression where pushing EOS into a blocked appsrc would stall, and glcolorconvert fixes compatibility with older OpenGL and GLSL versions. The mxfdemux element resolves keyframe detection regressions and possible artifacts after seeking, and rtpmanager fixes crashes on malformed RTCP SDES due to uninitialized values. The Rust-based plugins gain DoS protection in rtpsession and limit the number of remote sources tracked in rtprecv. Security fixes span multiple parsers including pnmdec and onnx, and the x264enc high bit depth support is fixed in binary packages.
ffmpeg 8: A massive security update carrying more than 20 CVE patches. Fixes address out-of-bounds reads and writes across numerous demuxers and decoders including HEVC, CineForm, TIFF, Screenpresso, and DVB subtitle parsers. The RTP muxer receives bounds checks for AV1, VC-2, and ASF objects, and the MPEG muxer rejects stream counts that overflow the system header. This is an essential update for any system that processes media files, as the vulnerabilities could be triggered by crafted input.
dracut: Received a security fix for CVE-2026-6893, a root code execution vulnerability via DHCP options command injection. The fix sanitizes values written to network override files, gateway files, and hostname files, and strips DHCP-supplied domains to a safe charset. This is important for any system that uses dracut-generated initrd images with network boot configurations.
Security Updates
rsync 3.5.1:
-
CVE-2026-53783: Fixes an
rrsyncrestricted-directory escape via a validation-versus-execution race and an unsafe option allowlist. -
CVE-2026-53784: Addresses a daemon module-root
chdirescape underuse chroot = no. -
CVE-2026-53785: Resolves
--relativeimplied-parent creation escaping the destination tree. -
CVE-2026-53786: Fixes a daemon
--filtermerge file bypassing the module filter list. -
CVE-2026-53788: Addresses the daemon name-converter accepting newline-bearing names into its line protocol.
-
CVE-2026-53789: Corrects a malicious sender expanding
--deletescope by reclassifying an implied parent. -
CVE-2026-53790: Fixes command and argument injection via unquoted peer- or host-controlled values.
-
CVE-2026-53791: Addresses PROXY-protocol mode letting a direct client spoof the daemon’s source address.
-
CVE-2026-53792: Resolves a receiver-supplied zero checksum block length driving the sender into a negative match.
-
CVE-2026-53793: Fixes a chroot
/./inner-module escape via a parent-component symlink. -
CVE-2026-53794: Addresses a remote peer disabling the per-allocation sanity cap via
--max-alloc=0. -
CVE-2026-53795: Corrects a receiver write escape via an absolute
--temp-diror--link-destdisabling rename and link confinement. -
CVE-2026-53796: Fixes a non-daemon receiver destination-
chdirsymlink race. -
CVE-2026-53797: Addresses a sender source-tree parent-component symlink race leading to out-of-tree disclosure.
-
CVE-2026-53798: Resolves the daemon name-converter mapping an unknown name to uid/gid 0 on an empty response.
-
CVE-2026-53799: Fixes receiver ACL and xattr application following a symlink race for arbitrary ACL setting and local privilege escalation.
-
CVE-2026-53800: Addresses sender
--remove-source-filesunlink following a parent-component symlink race for arbitrary file deletion outside the source tree. -
CVE-2026-53801: Corrects sender and daemon directory-scan enumeration escaping the transfer root for out-of-tree disclosure.
-
CVE-2026-53802: Fixes arbitrary file read and transfer shaping via symlinked operator-supplied input files.
-
CVE-2026-53803: Addresses arbitrary file write and privilege escalation via symlinked operator-supplied output paths.
-
CVE-2026-70463: Fixes
auth usersignoring documented comma-only parsing and silently skipping a deny or read-only rule. -
CVE-2026-70462: Addresses a peer-supplied
MSG_IO_TIMEOUTdefeating the client’s own I/O timeout through signed overflow and a non-positive value. -
CVE-2026-70461: Resolves a peer-driven one-byte heap out-of-bounds write in
add_implied_include(). -
CVE-2026-70460: Fixes a daemon module-root escape through a peer-supplied
--partial-diror--backup-dirresolving via an in-module symlink. -
CVE-2026-70459: Addresses a per-connection daemon child crash from a crafted first incremental file list with a non-directory transfer root.
-
CVE-2026-70458: Corrects an out-of-bounds write from a
FLAG_HLINKEDfile entry accepted without-H. -
CVE-2026-70457: Patches an attacker-chosen-offset write in
parse_size_arg()error formatting. -
CVE-2026-70456: Fixes a remote out-of-bounds heap write in
read_args()when the argument count lands exactly onmaxargs. -
CVE-2026-70454: Addresses
rsync-sslestablishing an unauthenticated TLS connection with no CA verification and no stunnel hostname binding. -
CVE-2026-70453: Resolves quadratic CPU exhaustion in
hash_search()from a crafted equal-weak-checksum chain. -
CVE-2026-70464: Fixes an unauthenticated pre-transfer handshake denial of service locking out an rsync daemon module.
-
CVE-2026-70455: Addresses peer-controlled Zstandard worker exhaustion on an rsync daemon.
-
CVE-2026-70452: Corrects
hosts denyfailing open when a configured hostname cannot be resolved, admitting the host it was meant to block. -
CVE-2025-10158: Fixes an out-of-bounds array access via a negative index.
-
CVE-2026-41035: Addresses a count of entries mismatch leading to a use-after-free.
-
CVE-2026-43617: Resolves authorization bypass via hostname resolution.
-
CVE-2026-43618: Addresses a second authorization bypass, tracked separately from CVE-2026-43617.
-
CVE-2026-29518: Fixes integer overflow information disclosure.
-
CVE-2026-43619: Addresses a symlink race condition via path-based syscalls.
-
CVE-2026-43620: Corrects an out-of-bounds array read via
recv_files(). -
CVE-2026-45232: Fixes an off-by-one stack out-of-bounds write in HTTP CONNECT proxy response parsing.
python313 3.13.15:
-
CVE-2026-19672: Fixes a
tarfilemember that leaves the destination directory and comes back. -
CVE-2026-17084: Addresses Unicode codepoint attributes outside RFC 3454 being considered valid.
-
CVE-2026-15308: Resolves quadratic complexity in incremental parsing of long unterminated constructs in
html.parser.HTMLParser, exploitable for denial of service. -
CVE-2026-6879: Corrects quadratic behavior in
xml.etree.ElementTree.Elementfindall(),iterfind()andfind()when using XPath index predicates on documents with many same-tag siblings. -
CVE-2026-4360: Fixes
tarfile.TarFile.extract()not applying the given filter when it extracts a link target from the archive as a fallback. -
CVE-2026-11972: Addresses
tarfileseeking a stream continuing past the end of the stream. -
CVE-2026-11940: Resolves a bypass of CVE-2025-4330 where crafted archives could create a symlink pointing outside the destination directory through the
tarfiledata and extraction filters. -
CVE-2026-0864: Corrects line endings in multi-line
configparservalues not being normalized to LF+TAB. -
CVE-2025-15366: Fixes NUL, CR and LF characters being accepted in IMAP commands.
-
libexpat 2.8.2: The bundled libexpat is updated to 2.8.2.
util-linux 2.42.3:
-
CVE-2026-76642: Fixes
mount(8)post-mount hooks executing after an external mount helper fails, allowing privileged operations on the pre-existing target filesystem. -
CVE-2026-78410: Addresses a
mount(8)time-of-check/time-of-use race on the source path in restricted SUID mode, letting a local attacker redirect a privileged mount or post-mount ownership change. -
CVE-2026-78409: Resolves an
X-mount.subdirsymlink escape from a detached mount tree inmount(8). -
CVE-2026-78408: Fixes a file descriptor leak in
nsenter(1)andunshare(1)where descriptors were not created withO_CLOEXEC. -
Hostname escape sequence injection: An additional fix for CVE-2024-28085 sanitizes the hostname interpolated into the
wall(1)andwrite(1)banner headers, which an unprivileged user could otherwise poison via a user namespace hostname.
tesseract-ocr:
-
CVE-2026-88047: Fixes a stack buffer overflow in
Classify::ReadNormProtoson a crafted traineddata file. -
CVE-2026-88048: Addresses a heap out-of-bounds write and read in
FullyConnected::Forwardvia a dimension mismatch. -
CVE-2026-88049: Resolves a heap out-of-bounds write in
LSTM::Forwardvia anna_/gate-matrix dimension mismatch. -
CVE-2026-88050: Fixes an out-of-bounds write in
UnicharCompressvia unvalidated recoder code values. -
CVE-2026-88051: Corrects a heap out-of-bounds write in
GenericVector<T>::readvia a reserved/size_used mismatch. -
CVE-2026-88052: Patches a heap out-of-bounds write in
UNICHARSET::load_via_fgetsvia a count/insert desynchronization. -
CVE-2026-88053: Addresses a heap out-of-bounds write in
Classify::ReadIntTemplatesvia unvalidated counts in a crafted traineddata file. -
CVE-2026-88054: Resolves a denial of service via an empty-stack dereference at model load.
-
CVE-2026-73067: Fixes a heap out-of-bounds read in
SquishedDawgon a crafted model, already patched in the shipped 5.5.3.
hplip 3.26.6:
-
CVE-2026-91097: Fixes a security vulnerability in the HP Linux Imaging and Printing utilities.
-
CVE-2026-91098: Addresses a security vulnerability in the HP printer and scanner backend components.
-
CVE-2026-91099: Resolves a security vulnerability in HPLIP’s firmware and device handling code.
-
CVE-2026-91100: Corrects a security vulnerability in the HPLIP scan backend.
-
CVE-2026-91101: Patches a security vulnerability in the HPLIP print queue and status handling.
-
CVE-2026-91102: Fixes a security vulnerability in the HPLIP device discovery code.
-
CVE-2026-91103: Addresses a security vulnerability in the HPLIP model and capability database.
-
CVE-2026-91104: Resolves a security vulnerability in the HPLIP fax and scan utilities.
-
CVE-2026-91105: Corrects a security vulnerability in the HPLIP plugin download and verification path.
-
CVE-2026-91106: Patches a security vulnerability in the HPLIP status and configuration tools.
freeipmi 1.6.19:
-
CVE-2026-85504: Fixes a stack-based buffer overflow via malformed Fujitsu SEL long-text responses.
-
CVE-2026-85505: Addresses a denial of service via a stack-based buffer over-read in
ipmi-oem. -
CVE-2026-85506: Resolves arbitrary code execution via a stack-based buffer overflow in
ipmi-oem. -
CVE-2026-85507: Fixes a stack-based buffer overflow in
_output_dell_system_info_cmc_info. -
CVE-2026-85508: Corrects a stack-based buffer overflow in
_output_dell_system_info_cmc_ipv6_info. -
CVE-2026-85509: Patches a stack-based buffer overflow when a BMC returns more bytes than requested.
gvfs 1.60.3:
-
CVE-2026-88924: Fixes the admin backend setting socket ownership after creation rather than before.
-
CVE-2026-84268: Addresses the sftp backend not clamping the
read_replycount to the requested buffer size. -
CVE-2026-84270: Corrects the mtp backend not validating the read size returned by the device.
flatpak 1.18.3:
-
CVE-2026-87766: Fixes a vulnerability in the bundled bubblewrap 0.12.0 sandbox component.
-
CVE-2026-93676: Addresses a vulnerability in the bundled xdg-dbus-proxy 0.1.8 filtering component.
libsoup:
-
CVE-2026-85534: Fixes libsoup 3 sending more body bytes than nghttp2 requested.
-
CVE-2026-85197: Resolves a crash in
on_data_readafter the connection has been destroyed. -
CVE-2026-77680: Corrects a flaw in HTTP Range header processing in libsoup 2.
-
CVE-2026-77014: Addresses the same HTTP Range header processing flaw in libsoup 2.
p11-kit 0.26.5:
-
CVE-2026-18938: Fixes an overflow when decoding nested attributes.
-
CVE-2026-13757: Addresses server-side stack exhaustion via unbounded recursion in RPC attribute parsing by enforcing a recursion depth limit.
sssd:
- CVE-2026-87853: Fixes cross-user impersonation in the IDP provider by correcting user matching in access token evaluation.
PackageKit 1.4.0:
-
CVE-2026-19816: Fixes the dnf5 backend executing
repo-removefor simulated transactions.
curl 8.22.0:
-
CVE-2026-13608: Fixes OpenLDAP SASL authentication bypass.
-
CVE-2026-18924: Addresses HTTP/2 server push use-after-free.
-
CVE-2026-19931: Resolves Negotiate ambient user connection reuse.
-
CVE-2026-80229: Fixes OpenSSL provider use-after-free.
-
CVE-2026-80230: Addresses OpenSSL pinning bypass.
-
CVE-2026-80255: Resolves secure cookie attribute bypass with tab character.
-
CVE-2026-82209: Fixes domain-scoped PSL domain cookie issue.
NetworkManager:
-
CVE-2026-10805: Fixes dhclient accepting unsafe characters in URLs and hostnames.
-
CVE-2026-19685: Addresses 802.1x rejecting
ca-pathfor private connections.
glibc 2.44:
-
CVE-2026-6791: Fixes stack-based buffer clash during tilde expansion in
wordexp. -
CVE-2026-6368: Resolves invalid call to
free()whenwordexpis used withWRDE_APPEND. -
CVE-2026-18374: Fixes a heap buffer overflow in the libio
ccs=handling. -
CVE-2026-19499: Addresses incorrect right-justification in
strfmon. -
CVE-2026-19542: Resolves an out-of-bounds array write in
tdelete. -
CVE-2026-77117: Fixes SHIFT_JISX0213 decoding leaving a pending character set across conversions.
-
CVE-2026-80489: Corrects the same pending character reset problem for EUC_JISX0213 decoding.
exiv2 0.28.9:
-
CVE-2026-68547: Fixes a security vulnerability in EXIF metadata processing.
-
CVE-2026-68546: Addresses a security vulnerability in image metadata handling.
-
CVE-2026-49275: Resolves a security vulnerability in the metadata library.
dracut:
- CVE-2026-6893: Fixes root code execution via DHCP options command injection.
libpcap 1.10.7:
-
CVE-2026-0799: Fixes safe M[] access in the BPF interpreter.
-
CVE-2026-31912: Addresses program bounds checking in
pcap_offline_filter(). -
CVE-2026-31911: Resolves safe opcode failure handling in the BPF interpreter.
-
CVE-2026-6244: Fixes division by zero via
pcap_offline_filter(). -
CVE-2026-6554: Addresses “ja L” looping limit in
pcap_offline_filter(). -
CVE-2026-18313: Fixes memory leak in rpcapd.
-
CVE-2026-18238: Addresses RPCAP_MSG_PACKET validation.
ffmpeg 8:
-
CVE-2026-75147: Fixes OBU size bounding in AV1 RTP keyframe search loop.
-
CVE-2026-75146: Addresses negative fragment index in DASH demuxer.
-
CVE-2026-75145: Resolves OBU size narrowing to
longin AV1 RTP muxer. -
CVE-2026-75144: Fixes data units larger than RTP payload buffer in VC-2 muxer.
-
CVE-2026-75143: Addresses caller buffer size honoring in librist reader.
-
CVE-2026-75142: Resolves stream count overflow in MPEG muxer.
-
CVE-2026-75141: Fixes hvcC NAL array overflow in HEVC demuxer.
-
CVE-2026-70632: Addresses transform-2 output width validation in CineForm decoder.
-
CVE-2026-70631: Resolves inflate output length check in TIFF decoder.
-
CVE-2026-70630: Fixes deflate output length check in Screenpresso decoder.
-
CVE-2026-70629: Addresses uninitialized data on short input in rscc decoder.
-
CVE-2026-70628: Resolves signed overflow in DVB subtitle parser capacity check.
-
CVE-2026-66037: Fixes count_label validation in IAMF parser.
-
CVE-2026-66036: Addresses dynamic frame size support in hqdn3d filter.
-
CVE-2026-65706: Fixes temp row buffer sizing in swaprect filter.
-
CVE-2026-65705: Resolves unneeded variables in floodfill filter.
-
CVE-2026-65704: Fixes AC3 trim underflow in Ty demuxer.
-
CVE-2026-65703: Addresses reference frame handling in TDSC decoder.
-
CVE-2026-64834: Resolves ASF object size validation in RTP decoder.
-
CVE-2026-64833: Fixes DTS core_size bounding in SPDIF encoder.
-
CVE-2026-58049: Addresses DLTA access bounds checking in RASC decoder.
389-ds 3.3.1:
-
CVE-2026-18355: Fixes heap buffer overflow in the SASL I/O layer.
-
CVE-2026-18663: Addresses pre-authentication double-free via critical Session Tracking control.
-
CVE-2026-11770: Resolves pre-auth LDAP filter injection in CleanAllRUV status check.
-
CVE-2026-18453: Fixes pre-authentication NULL pointer dereference via paged results.
-
CVE-2026-15722: Addresses pre-authentication stack buffer overflow via unbounded replica ID parsing.
-
CVE-2026-18922: Resolves stale identity installation following SASL PLAIN authentication.
-
CVE-2026-19843: Fixes Cockpit LDAP editor shell command injection.
-
CVE-2026-76560: Addresses SELFDN ACI bind-rule evaluator incorrect matching.
xen 4.22.0_04:
-
CVE-2026-62437: Fixes memory leak caused by device model IRQ binding.
-
CVE-2026-79602: Addresses improper handling of HVM emulation return codes.
-
CVE-2026-79603: Resolves TLB flushing not happening before page scrubbing.
coreutils:
-
CVE-2026-56391: Fixes read buffer overrun in
uniq -win multibyte locales. -
CVE-2026-56392: Addresses heap overflow in
unexpand -tfor tab values larger thanSIZE_MAX/16.
gegl 0.4.72:
- CVE-2026-18300: Fixes vulnerability in the RGBE loader for large report files.
cups-filters:
-
CVE-2026-64611: Fixes infinite-loop CPU-exhaustion denial of service in
cfIEEE1284NormalizeMakeModelon empty MDL field. -
CVE-2026-64612: Addresses malformed PNG aborting the CUPS image filter process due to missing libpng setjmp recovery.
alsa:
- CVE-2026-90781: Fixes a denial of service via an off-by-one stack buffer overflow in the control interface parser.
cups 2.4.19:
-
CVE-2026-87875: Addresses a heap out-of-bounds read in
cupsUTF32ToUTF8()due to a missing source-length bound, reachable from SNMP supply-description parsing.
7-Zip 26.03:
- CVE-2026-58052: Fixes 7-Zip failing to preserve the Mark-of-the-Web when extracting a crafted archive, which let an extracted file bypass the trust check meant to keep it quarantined.
GIMP 3.2.6:
- CVE-2026-80101: Fixes invalid guards on XWD parameters, which could lead to a buffer overflow when loading a crafted XWD file.
discount 3.0.2.0:
-
CVE-2026-4833: Addresses uncontrolled recursion in
compile()on deeply nested input, leading to stack exhaustion and a crash. The parser now caps nesting depth, defaulting to 200 and tunable via--with-recursion.
libX11:
-
CVE-2026-88806: Fixes a heap-based buffer overflow in the
XkbGetMapreply by checking the keysym range in_XkbReadKeyActions.
libXrender:
-
CVE-2026-88807: Fixes an out-of-bounds write into
screen->subpixelwhen a malicious server replies toXRenderQueryFormatwith anumSubpixelscount greater than the number of screens.
libtpms:
-
CVE-2026-85769: Fixes a heap out-of-bounds read in TPM2 state unmarshalling via an unchecked
block_skip_read()blocksize.
librsvg 2.62.4:
- Use-after-free with nested Xinclude: Fixes a use-after-free when duplicate XML entities appear in nested Xinclude documents.
Users are advised to update to the latest versions to mitigate these vulnerabilities.
Conclusion
September was a busy month for openSUSE Tumbleweed with snapshots delivering a steady cadence of desktop, developer, and security improvements. KDE Plasma 6.7.5 and KDE Frameworks 6.30.0 refined the KDE desktop and added new features, while KDE Gear 26.08.1 stabilized the application suite with fixes across Dolphin, Okular, and Kitinerary. glibc jumped to 2.44 with Transparent Huge Pages tunables and vectorized math functions, and LLVM 23.1.1 arrived with important toolchain bugfixes. The Linux kernel progressed through 7.2.4 with extensive CVE coverage across USB, networking, and virtualization subsystems, and Mesa settled into its 26.2.2 release. LibreOffice advanced to 26.8.0.3 and harfbuzz improved text shaping performance and correctness. The second half of September carried the month’s heaviest security load. rsync 3.5.1 arrived after an audit of its path handling and daemon protocol that turned up more than 40 vulnerabilities, including a set of chroot and rrsync escapes, a hosts deny rule that failed open when a hostname could not be resolved, and an unauthenticated handshake denial of service against a daemon module. On the desktop side, the GNOME stack picked up 50.5 across gnome-shell and mutter, GIMP advanced to 3.2.6, Shotwell reached 33.0, bash-completion 2.17.0 and coreutils 9.12 landed alongside a burst of late-month updates across Mesa 26.2.3, PipeWire 1.6.9, Poppler 26.09.0, BlueZ 5.87, and xz 5.8.4.
Slowroll Arrivals
Please note that these updates also apply to Slowroll and arrive between an average of 5 to 10 days after being released in Tumbleweed snapshot. This monthly approach has been consistent for many months, ensuring stability and timely enhancements for users. Updated packages for Slowroll are regularly published in emails on openSUSE Factory mailing list.
Contributing to openSUSE Tumbleweed
Stay updated with the latest snapshots by subscribing to the openSUSE Factory mailing list. For those Tumbleweed users who want to contribute or want to engage with detailed technological discussions, subscribe to the openSUSE Factory mailing list . The openSUSE team encourages users to continue participating through bug reports, feature suggestions and discussions.
Your contributions and feedback make openSUSE Tumbleweed better with every update. Whether reporting bugs, suggesting features, or participating in community discussions, your involvement is highly valued.
Welcome to openSUSE Asia Summit in Yogyakarta
The wait is almost over! 🎉
The openSUSE.Asia Summit 2026 will begin on Oct. 3-4 at UIN Sunan Kalijaga, Yogyakarta.
On behalf of the organizing committee, we would like to warmly welcome everyone to Yogyakarta and to this year’s Summit. We hope you enjoy the talks, workshops, discussions, and all the activities we have prepared for you.
For those visiting Yogyakarta for the first time, don’t forget to enjoy the city as well. Take some time to explore its food, culture, streets, and atmosphere. Yogyakarta has plenty to offer beyond the conference venue.
And for those meeting old friends again, we hope this summit becomes a warm opportunity to reconnect, catch up, share stories, and spend some good time together with the community. ❤️
Let’s make openSUSE.Asia Summit 2026 a memorable gathering!
Welcome to Yogyakarta, and enjoy the Summit! 🦎💚
Kudos Now Recognizes Whole Teams
The openSUSE Kudos recognition platform has a new feature: teams. You can now thank a whole team at once, see who is part of which team, and join or start a team yourself.

Why teams
Peer-to-peer recognition is at the heart of Kudos, and it works well when the work was done by one person. A lot of what happens in openSUSE is not like that, though. A release, an installer, a conference booth or a wiki cleanup is usually the effort of an entire group.
One piece of feedback kept coming back: when someone wanted to thank a team, the kudos landed on the one or two people they happened to know by name. The rest of the people who did the work got nothing, simply because the person saying thanks could not name them.
Some contributors are also simply less visible than others. They do not post much, they do not show up in every chat, and their work happens quietly in the background. That does not mean they do less. Recognizing the team as a whole makes sure that thanks reaches them too.
What you can do
- Thank a team, or a team and individuals together. When giving kudos, teams show up in the recipient picker next to people. You can thank a team on its own, or combine it with individual contributors in the same kudo. That comes in handy because teams rarely work alone: a release team may get help from translators, testers or packagers outside the team, and now one thank-you can include all of them. Team members can thank their own team as well.
- See who is in which team. Every team has its own page with its roster, and every profile now shows the teams that person belongs to. Former members stay listed as alumni, so past contributions are not forgotten.
- Join or start a team. Click the Join Team button in the header, search for your team, and ask to join. If your team is not there yet, create it right from the same box. No admin approval is needed to start a team; only linking it to a badge goes through an admin (more on that below).
- Invite people. Team members can invite other Kudos users by their username. The invitation arrives by email and in the app, and the person joins once they accept.
Once you are in a team, the button in the header turns into My Teams, and it lets you know when an invitation or a join request is waiting for you.
Self-managed teams
Teams run themselves. There is no owner and no manager role. Any member can approve people who asked to join, invite others, or tidy up the roster, and anyone can leave at any time. Requests that nobody answers are approved automatically after 14 days, so nobody gets stuck waiting.
Teams can also be linked with a badge. This is the one step that needs an admin, and for a good reason: a linked badge adds every holder of that badge to the team. If anyone could link any badge, a brand-new team could claim the Tumbleweed contributor badge and instantly “have” hundreds of members who never asked to join. So an admin checks that the badge really belongs to the team before linking it.
Once an admin links a badge to a team, everyone on the roster gets it, and anyone who later earns the badge through other means is added to the team automatically. Until now, team badges were handed out by hand, one person at a time. Now the team keeps its own roster, and the badge follows.
Every team page has a badge slot, and for most teams it still reads “Badge: TBD”. Badges live in openSUSE/kudos-badges on GitHub, where new ideas and artwork arrive as ordinary pull requests, so a team that wants to fill its slot is only a pull request away. Designing the badge together can be a fun first thing for a new team to do.
Badges are never taken away when someone leaves a team. A badge records what you did; the team roster shows who is there now.
Get started
Log in to kudos.opensuse.org, click Join Team, and find your team or start a new one. Then invite the people you work with, and the next time your team ships something great, thank all of them at once.
Feedback is welcome, as always. Kudos is developed in the open at github.com/openSUSE/kudos.
validate_script_output over grep
In OpenQA one has often to check the output of a command. Now most of us think foremost “this is a task for my beloved grep”:
Tiny Wins for Packagers: End-of-Week Update (2026-09-25)
Deadline Extended Call for Host openSUSE Asia Summit 2027
The openSUSE.Asia Summit Organizing Committee has extended the deadline for the Call for Host to submit proposals for the 2027 Summit. Communities now have until 30 November, 2026 to apply.
The extension comes in response to requests from local communities seeking more time to prepare their proposals. This is a great opportunity to showcase your region and bring the openSUSE community together in your city.
If your community is interested in hosting the openSUSE.Asia Summit 2027, come and join us at openSUSE.Asia Summit 2026 in Yogyakarta this October. The organizing committee can provide presentation slots for communities interested in hosting the 2027 Summit, giving them an opportunity to introduce their community, city, and vision for the next Summit.
For more information, visit https://news.opensuse.org/2026/07/14/osas-cfh/.
Try Immutable Mode with openSUSE Leap 16.1 RC
Entering RC Phase
openSUSE Leap 16.1 has entered the Release Candidate phase. Release Candidate images can be found at get.opensuse.org.
We know that people really start testing a new release with the RC, so this is the right time to grab an image and give it a try.
Users can expect that we’ll continue publishing roughly one build a week during the RC phase. Once SUSE Linux Enterprise Server 16.1 announces their Gold Master, we’ll be working toward the Leap 16.1 Gold Master Candidate (GMC).
Based on feedback from the Leap 16.0 retrospective, we’ll sync the Leap 16.1 release day with the SLES 16.1 release day, even if that means a slight delay. This way, there is no obvious gap in receiving maintenance updates after the release.
Details about the schedule can be found in our roadmap.
Usecase: Try the new Immutable mode
Leap 16.1 is the first Leap release to offer an Immutable Mode, a transactionally updated system with a read-only root filesystem. This is essentially what our users know from Leap Micro, just integrated directly into Leap.
Leap 16.1 in Immutable mode is replacing Leap Micro. There won’t be a Leap Micro 6.3 or 7.0; Leap Immutable is the way forward for container and virtual machine hosts, edge devices and anyone who prefers atomic updates with easy rollback.
The Immutable mode was added to Agama rather recently, which is exactly why we’d like you to try it. Simply boot the usual Leap 16.1 install image and pick the Immutable mode in the installer.
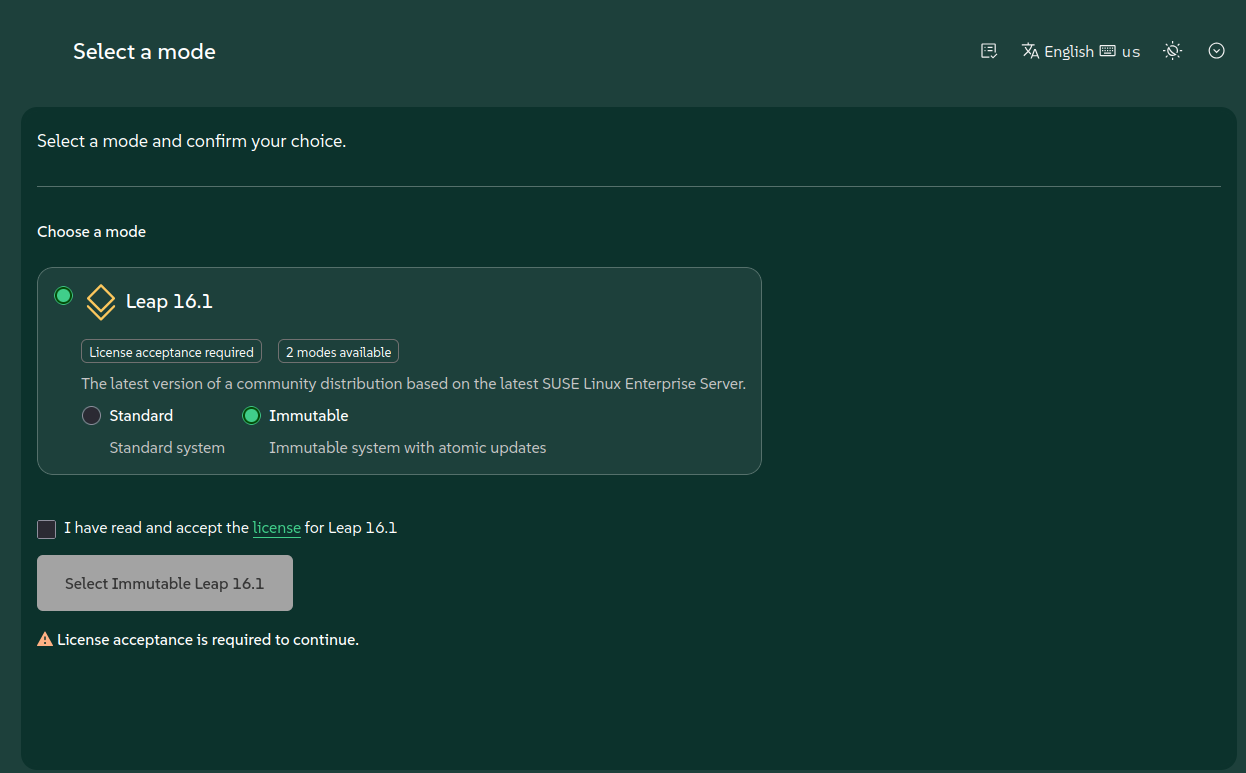
Doesn’t agama with dark theme look amazing? Once installed, the system is updated with transactional-update, which creates a new snapshot for every update and lets you roll back if something goes wrong.
sudo transactional-update dup    # update the system into a new snapshot
sudo reboot                      # boot into the new snapshot
sudo transactional-update rollback  # go back if something went wrong
Additional software is best consumed via containers with podman or distrobox, or via Flatpak on desktops. Packages can still be installed with sudo transactional-update pkg install <package>.
Leap Micro users: appliances are still here
Users who are used to the Leap Micro images will feel at home. The usual preconfigured appliances can be found in the alternative downloads section at get.opensuse.org. This includes the Immutable Self-install image, which is recommended for USB installations, as well as images for KVM/Xen, MS Hyper-V, VMware, Harvester and Cloud, and a fully encrypted raw disk image.
The appliances can be configured on first boot via Ignition or Combustion, just like Leap Micro.
Existing Leap Micro 6.2 installations can be migrated to Leap 16.1 in Immutable mode with the opensuse-migration-tool.
sudo transactional-update shell
# Inside the shell:
zypper in opensuse-migration-tool
opensuse-migration-tool --dry-run # optionally check how it looks
opensuse-migration-tool
exit && reboot # boot into the new snapshot
The tool is still experimental, so please make sure to have a backup and let us know how the migration went.
Desktops: Same GNOME, newer Plasma
Some users may expect a big GNOME update in Leap 16.1. In fact, Leap 16.1 ships the same GNOME 48 as Leap 16.0, with bug fix updates (gnome-shell 48.8 vs. 48.4 in 16.0).
Just like in Leap 15.X and the respective SUSE Linux Enterprise 15 service packs, the big GNOME update is planned over two releases.
Leap 16.0 and 16.1 share the same GNOME major version, and users can expect the next big GNOME update in a future release.
KDE Plasma users, on the other hand, get a noticeable bump from Plasma 6.4 to Plasma 6.6 with Qt 6.11 and KDE Frameworks 6.25.
LXQt moved from 2.2 to 2.4, and Xfce on Wayland continues with 4.20.
What’s new in Leap 16.1
Wondering which version of your favorite package you’ll get in Leap 16.1? Rather than listing a handful of packages here, we’d like to point you to our new openSUSE version diff tool.
It’s a single page comparing source package versions across Leap 16.1, Leap 16.0 and Tumbleweed, including the latest upstream versions from Repology.
The page republishes itself automatically, so it stays up to date during the whole RC phase and beyond. You can filter packages by status, e.g. to see what was updated compared to 16.0, or download the data as JSON or CSV.
The tool grew out of a community discussion at our weekly Release Engineering meeting; read more about it in One Page, Every Package.
Ideas and contributions are welcome at github.com/openSUSE/osdiff.
Help us with testing
Your feedback is critical at this stage. Help us with testing by following our manual test plan.
The plan covers scenarios that are hard to automate in openQA, so every test case marked as done on as many hardware combinations as possible helps us to ship a better release.
Simply record your result with your openSUSE ID; we intend to award Kudos badges to everyone participating in manual testing.
Alternatively, simply install Leap 16.1 RC, try the Immutable mode, your favorite desktop or your usual server workload, and let us know how it goes.
Please report any issues on bugzilla.opensuse.org.
Please make sure to check the Known bugs wiki page prior to reporting a new bug.
Thank you for testing and being part of the openSUSE community. Let’s shape Leap 16.1 together!

Speeding up tests - no fear, no cargo cult
The openQA test suite for openSUSE and SLE has about 2,400 test modules and 1,500 schedule files. Over a 12-month window they run a few million times and burn about 710,000 machine-hours of worker time across two instances, the public openqa.opensuse.org and SUSE’s internal openQA. For the last two months I have been trying to shrink that number, cheap wins first.
I kept finding fossils. A comment header in hostname describing code deleted in 2019. A network restart timeout that crept from 10 to 120 seconds over two years of bug reports. A make -B workaround from 2018 for a bug fixed upstream that same year. Each made sense when it was written. But they add up, and they run on every job.
 Vojtaeus
Kurz práce v příkazové řádce Linuxu nejen pro MetaCentrum 2027
Don't be afraid of the command line! It is a friendly and powerful tool, allowing you to process large data and automate tasks. Practically identical is command line also in Apple macOS, BSD and other UNIX-based systems, not only in Linux. The course is designed for total beginners as well as intermediate advanced students. The only requirement is an interest (or need) to work in command line, typically on Linux computing servers.

 Member
Tumbleweed – Review of the week 2026/39
Dear Tumbleweed users and hackers,
This week was another busy and productive cycle, seeing the publication of 6 snapshots (0917, 0918, 0919, 0921, 0922, and 0923) to keep your rolling distributions completely fresh.
Leading the charge on the desktop side, web browsing received a welcome boost with the arrival of Mozilla Firefox 156.0, while GNOME users were treated to nice polish with point updates to GNOME Shell 50.5, Mutter 50.5, and Libadwaita 1.9.4. Under the hood, Linux Kernel 7.2.6, Mesa 26.2.3, and PipeWire 1.6.9 kept the core hardware, graphics, and multimedia foundations moving along smoothly.
Alongside the big-name releases, package maintainers have kept the updates flowing steadily to keep the distribution secure and robust, with welcome updates arriving for AppStream 1.2.0, PackageKit 1.4.0, util-linux, and Python 3.13.
These 6 snapshots delivered the following updates:
- AppStream 1.2.0
- bluez 5.87
- cppcheck 2.22.0
- cryptsetup 2.8.8
- feh 3.13.1
- freerdp 3.31.1
- glslang 16.6.0
- gnome-shell 50.5
- gzip 1.15
- harfbuzz 14.5.0
- hplip 3.26.6
- ImageMagick 7.1.2.31
- jemalloc 5.4.0
- kdump 2.1.10
- libadwaita 1.9.4
- libgsf 1.14.59
- libheif 1.23.5
- libinput 1.32
- libsolv 0.7.40
- libsrtp2 2.8.1
- libstorage-ng 4.5.354
- libupnp 22.1.2
- libzio 1.17
- libzypp 17.38.16
- lightdm 1.33.1
- lightdm-gtk-greeter 2.0.9
- Linux Kernel 7.2.6
- Mesa 26.2.3
- mozilla-nss 3.128
- MozillaFirefox 156.0
- mutter 50.5
- ncurses 6.6.20260919
- nvme-cli 3.1
- p11-kit 0.26.5
- PackageKit 1.4.0
- perl-Cpanel-JSON-XS 4.520.0
- perl-GD 2.910.0
- pipewire 1.6.9
- pulseaudio-qt6 1.9.0
- Python 3.13.15
- python-greenlet 3.5.6
- python-tornado6 6.5.10
- rsync 3.5.1
- shaderc 2026.4
- snappy 1.3.0
- suitesparse 7.14.1
- thin-provisioning-tools 1.3.4
- util-linux 2.42.3
- VirtualBox 7.2.18
- xscreensaver 6.16
- xwaylandvideobridge 0.5.3
- xxhash 0.8.4
Looking beyond these releases, here is what is currently working its way through staging:
- Linux Kernel: Both 7.2.7 and 7.2.8 updates are on their way, with 7.2.7 already lined up and 7.2.8 progressing through staging.
- KDE Plasma 6.8 Beta: Currently being tested, working through build and installcheck hurdles.
- expat: Blocked by build failures in perl-XML-Twig.
- systemd: Currently blocked on a security review of its D-Bus services.
- Swig 4.5.0: YaST integration issues remain under investigation, with yast2-network, yast2-nfs-client, and yast2-storage-ng currently failing builds.
- fontconfig 2.18.3: Still held up as it breaks the AppStream test suite.
- libnettle 4.0.0: Remains explicitly excluded from main staging runs while developers work on resolving test suite breakages in libzypp.