Member
 Victorhck
Presvisualizar archivos MarkDown en el editor Kate de #KDE
Veamos cómo previsualizar el renderizado de archivos en formato markdown en el editor Kate de KDE

Utilizo mucho los archivos en formato markdown y si no los edito en la terminal mediante Vim utilizo Kate como editor principal. Y me acabo de enterar que Kate posee la opción de poder previsualizar el resultado del renderizado de markdown. Veamos cómo.
Abrimos Kate → Preferencias → Configurar Kate → Complementos
Y activamos el complemento «Vista previa del documento» y aceptamos los cambios. Ahora en la parte derecha aparecerá un icono de vista previa. O en el menú Ver → Vista de herramientas → Mostrar vista previa
Esto abrirá un panel lateral que renderizará los archivos Markdown ofreciendote una vista previa de cómo quedará, mientras que en el panel donde se edita tendrás el resaltado de sintaxis.
También lo he probado con archivos en formato HTML, pero no ha funcionado. Para ese formato quizás sea mejor seguir utilizando un navegador.
Y esto es todo lo que quería compartir por hoy.

Nightly syslog-ng containers based on Alma Linux
For many years, the syslog-ng project provided container images based on Debian. Most of our users run syslog-ng on RHEL & compatibles, and have asked for an RPM-based container. So, nightly containers based on Alma Linux are now also available.
A while ago, I prepared a small test project to run syslog-ng in an Alma Linux container: https://www.syslog-ng.com/community/b/blog/posts/experimental-syslog-ng-container-image-based-on-alma-linux However, that was only an experiment which I never updated. Fast forward to today: nightly syslog-ng containers based on the latest syslog-ng git snapshot package builds are now available on the Docker Hub!
Read more at https://www.syslog-ng.com/community/b/blog/posts/nightly-syslog-ng-containers-based-on-alma-linux
syslog-ng logo
Accepted into Google Summer of Code 2026 with openSUSE!
I am extremely excited to announce that I have been selected to participate in Google Summer of Code (GSoC) 2026! I will be contributing to the openSUSE Project.
The Project: Enhancing openSUSE Git Workflow
During the next 12 weeks, I will be working on improving the obs-status-service. Under the mentorship of Daniel García Moreno (dgarcia) and Doug, my main objectives include:
- Improving Visualizations: Extending the Go tool to generate better SVG images with new CSS styles and making them interactive with JavaScript.
- Gitea Bot Integration: Implementing a new bot for Gitea that provides useful build information directly inside Pull Requests.
- AI Integration (Stretch Goal): Exploring the use of AI through Log Detective to analyze and assist with PRs that fail to build.
Moving Forward
Given the dynamic nature of the GSoC program and software development itself, it’s very likely that these initial goals will adapt and change slightly as the weeks go by.
I’m ready to learn, face new challenges, and contribute to the open-source community. Stay tuned, as I will be posting my weekly progress right here!
qSnapper: Various Security Issues in Privileged D-Bus Service (CVE-2026-41045 through CVE-2026-41048)
Table of Contents
- 1) Introduction
- 2) Overview of the qSnapper D-Bus Service
-
3) Security Issues
- 3.1) Weak Polkit Authentication Check is Subject to Race Condition (CVE-2026-41045)
- 3.2) Path Traversal via
configNameParameter (CVE-2026-41046) - 3.3) Information Leak via “diff” Methods (CVE-2026-41047)
- 3.4) Caching of Authentication allows Authentication Bypass (CVE-2026-41048, CVE-2026-41049)
- 3.5) Defense-in-Depth Issues when Restoring Arbitrary Files
- 3.6) Other Issues
- 4) Upstream Bugfixes
- 5) Disclosure Process
- 6) Timeline
- 7) References
- Change History
1) Introduction
qSnapper is a GUI frontend for the snapper utility for managing Btrfs filesystem snapshots. In April we received a review request for qSnapper, because it contains a privileged D-Bus service and Polkit policies.
Normally, Btrfs snapshots can only be managed with root privileges. qSnapper aims to provide more user-friendly and fine-grained access to snapshot management features, based on a privileged daemon which utilizes D-Bus and Polkit. Our review of the service uncovered various security issues, which led to a longer coordinated disclosure to allow upstream to develop bugfixes, which are part of upstream release 1.3.3.
The full details of the security issues will be covered in the sections below. The original review was performed on qSnapper release 1.1.3. Since bigger upstream changes appeared in the meantime this report is based on qSnapper release 1.3.2, however.
2) Overview of the qSnapper D-Bus Service
The qSnapper project contains a daemon named qsnapper-dbus-service, which
runs with full root privileges. The daemon provides the D-Bus interface
“com.presire.qsnapper.Operations” on the system bus; some of its methods
are provided to arbitrary users in the system without authentication, while the
majority of them is protected by Polkit authentication checks. The
implementation of the various D-Bus methods offered by the service is found in
snapshotoperations.cpp. All of the security issues
outlined below are located in this compilation unit.
3) Security Issues
3.1) Weak Polkit Authentication Check is Subject to Race Condition (CVE-2026-41045)
The SnapshotOperations::checkAuthorization()
function uses Polkit’s UnixProcess subject in an unsafe way to authenticate
clients. The code obtains the client’s PID from the active D-Bus connection,
which leads to a race condition. At the time the Polkit daemon (polkitd)
checks the provided PID, the process in question can already have been
replaced by another, privileged process. This is a well-known class of Polkit
authentication bypasses which was assigned CVE-2013-4288.
In effect this means that clients may be able to bypass all Polkit
authentication checks performed by qSnapper, although the attack is somewhat
complex and might need multiple attempts to succeed. There is nothing stopping
a local attacker from doing that, however. In combination with the configuration
path traversal in D-Bus methods like
WriteSnapperConfig() described below, this can be used to achieve a full
local root exploit.
To fix this, we suggested to use Polkit’s SystemBusName subject instead. With
this subject, the D-Bus daemon obtains the client’s UID in a race-free fashion
from the UNIX domain socket the client used to connect, and polkitd cannot be
fooled by recycled PIDs.
3.2) Path Traversal via configName Parameter (CVE-2026-41046)
All the D-Bus methods accepting a configName parameter
(that is nearly all of them) suffer from a path traversal vulnerability. This
string parameter is directly passed to snapper::Snapper(), which is part of
the libsnapper API, without checking its safety. libsnapper expects a basename
here to look up a configuration file in /etc/snapper/configs. In the context
of qSnapper this string can contain additional path components like
../../path/to/crafted.cfg. This allows clients to use arbitrary
configuration files as input to libsnapper.
When looking at the writeSnapperConfig() D-Bus method, which requires admin authentication, this path traversal allows to write largely attacker-controlled data to arbitrary locations. Combined with the Polkit authentication bypass described earlier in section 3.1, this would allow for a full local root exploit.
In case of other D-Bus methods which use the “list-snapshots” Polkit action, the path traversal is also accessible to locally logged-in users without any authentication. Luckily the libsnapper configuration file format offers no features that lead to a trivial local root exploit in this context. The impact of the vulnerability can be any of the following, however:
- local Denial-of-Service (DoS): by pointing libsnapper to a special file like
/dev/zero, the daemon will consume the maximum amount of memory and be killed by the kernel. By pointing libsnapper to a named FIFO special file, the daemon will block indefinitely. - information leak from parsing of private files: by pointing libsnapper to a
private file like
/etc/shadow, libsnapper will parse the sensitive data from the file as configuration data. If any logging features are active and the logs can be accessed by unprivileged users, then private data from such a file might leak into the unprivileged context. We are not aware of such an information leak in default installations, however. - by providing crafted configuration data further attacks can be carried out:
-
SUBVOLUMEcan be pointed to arbitrary mounts in the system. Luckily libsnapper is conservative in its file operations here, and quite strictly verifies the validity of this path; it verifies if it is really a mount point and is backed by the expected block device and file system etc. -
ALLOW_USERSandALLOW_GROUPScan be set to arbitrary users and groups, allowing them officially to control the Snapper configuration. - The
SYNC_ACLsetting causes libsnapper to apply ACL entries to the.snapshotsdirectory of the volume path, granting the users and groups fromALLOW_USERSandALLOW_GROUPSto access the snapshot data. Thus this is a major local information leak.
-
libsnapper is using different backends depending on the file system type. Different code is used for each backend, which means that the exploitability of some aspects of the vulnerability depends on which backend is used. On openSUSE only the Btrfs and LVM thin volume backends are compiled-in by default, which only offer little additional attack surface.
To fix the issue, we suggested to upstream to verify the configName
parameter in all cases and reject it if any / or .. components are
found in it.
3.3) Information Leak via “diff” Methods (CVE-2026-41047)
The Polkit action “list-snapshots” is allowed for locally logged-in users without authentication, and is used by multiple qSnapper D-Bus methods which are likely considered “read-only” operations not harmful to the system. In version 1.1.3 of qSnapper the following methods are relying on this Polkit action:
ListSnapshots()GetFileChanges()GetFileDiffAndDetails()
In version 1.3.2 of qSnapper these additional methods are using the action:
GetFileChangesBetween()GetFileDiffBetween()
These methods allow to obtain information about metadata changes of arbitrary
files between snapshots or between snapshots and the live filesystem. The
newer GetFileDiffBetween() method even offers full file content diff output.
These are major local information leaks, since unprivileged users can get a
diff e.g. of the /etc/shadow file between different system states, or
changes from root’s home directory which could leak sensitive data like
passwords or private keys.
To fix this, we suggested to upstream that all methods providing non-public
information get restricted by auth_admin Polkit checks. Alternatively, a check
could be implemented whether the files to be diffed are normally accessible to
the caller by using checks similar to the access() system call; such an
approach would likely be rather complex and error-prone, however.
3.4) Caching of Authentication allows Authentication Bypass (CVE-2026-41048, CVE-2026-41049)
In version 1.2.1 of qSnapper an m_authenticated flag was introduced to the
daemon’s code, which caches authentication once a client has passed certain Polkit
action authentication checks. This cached authentication is shared between the
methods DeleteSnapshot(),
RestoreFiles() and
RestoreFilesDirect(). There are two issues
with this approach:
-
DeleteSnapshot()uses the “delete-snapshot” action, while the other methods use the “rollback-snapshot” action. If a caller can authenticate for “delete-snapshot” then it is also implicitly authenticated for “rollback-snapshot” and vice versa. This is not how Polkit is intended to be used. If a system administrator decides to relax the authentication requirement for “delete-snapshot”, then this automatically implies the “rollback-snapshot” action now, which are two very different impacts to the system. We assigned CVE-2026-41048 for this aspect of the issue. - The implementation of the caching logic assumes that a single interactive
client is talking to the daemon. In fact, arbitrary users can invoke
these methods. If a legitimate client is authenticated for one of the affected
actions once, then arbitrary other users like
nobodyare now also considered authenticated and Polkit will not be invoked anymore. This authentication bypass allows for a full local root exploit in the context of theRestoreFiles()methods, as outlined below in section 3.6. We assigned CVE-2026-41049 for this aspect of the issue.
We suggested to upstream to drop this form of authentication caching, or alternatively implement an authentication cache tied to each user and each Polkit action in question to avoid the issues.
3.5) Defense-in-Depth Issues when Restoring Arbitrary Files
This section discusses Defense-in-Depth issues which remain once all the
more tangible issues discussed above are fixed. The
restoreFiles() D-Bus method accepts arbitrary
filePaths as parameter to be restored from a version found in a snapshot.
Clients need to authenticate as an administrator to do this, so there is no
direct attack surface. Let’s consider the path /var/lib/colord/mapping.db to
be restored, however:
# On openSUSE Tumbleweed this directory is owned and writable by `colord`
$ ls -lh /var/lib/colord
drwxr-xr-x 3 colord colord 4.0K Mar 6 2024 .
At the time the qSnapper service performs the
chown() system call, the colord service user can
stage a symlink attack in the colord directory and cause arbitrary files in
the system to receive colord ownership, allowing a colord to root
exploit. A similar issue affects the copyRegularFile()
function, where a file on the live file system is
newly created.
This issue is hard to fix, given the many different file system situations
that the restore operation can end up in. The basic algorithm to address the
problem would need to use low-level system calls like openat(), fchown()
and fstatat() to safely traverse file system paths and inspect any symbolic
links on the way. Given the complexity of the bugfix and limited impact, we
agreed with the upstream author that this fix does not need to be prepared
during the coordinated disclosure period but can be developed in the open
afterwards.
Given the amount of front-line security issues already found in qSnapper in the course of this review, we refrained from assigning a dedicated CVE for these Defense-in-Depth issues in this case.
3.6) Other Issues
This section covers a number of other issues that are not fully-fledged security issues, but still represent weaknesses or possible hardenings for the qSnapper implementation.
- the D-Bus method
RestoreFiles()implements complex file operations to rollback changes of a file path to the state found in a snapshot. These file operations allow authenticated clients to achieve nearly arbitrary file operations:- recursive deletion of arbitrary paths
- copy of arbitrary files to arbitrary locations
- change of ownership of files to arbitrary users
- change of the file mode to arbitrary values
This is because the method is not verifying whether the claimed file exists in the snapshot in the first place and whether the
filePathscontain any../directory components to escape the snapshot directory. While this method is protected by Polkit’sauth_adminsetting, any D-Bus method should be written conservatively and in such a way that the intended purpose of the method cannot be bypassed. The very similar methodRestoreFilesDirect()has the same issues and also contains a lot of duplicate code which should be merged with the other method’s code. - the Quit() method can be called by anyone in the system without authentication. This is kind of a local DoS against an active qSnapper daemon in use by other users in the system.
- the logfile created in
/var/log/qSnapperwill be world-readable, which could leak sensitive information. For hardening purposes it could be made private toroot.
4) Upstream Bugfixes
The upstream author closely followed our suggestions to fix the security issues described in this report. Version 1.3.3 of qSnapper contains the following bugfixes:
-
commit a6caf538 addresses the following
issues:
- the Polkit
UnixProcesssubject is replaced by theSystemBusNamesubject to avoid the race condition during authentication (issue 3.1). - the
configNameparameter in all D-Bus methods is now carefully verified and rejected if it allows path traversal (issue 3.2). - the authentication caching is removed (issue 3.4).
- the
RestoreFilesmethods reject path traversal attempts (see section 3.6).
- the Polkit
-
commit f375b74c addresses the
following issues:
- a new
view-diffPolkit action is introduced to generate file diffs which requiresauth_adminauthentication to prevent information leaks (issue 3.3). - the unauthenticated
QuitD-Bus method was dropped (see section 3.6). - log files are now created without world-readable bit (see section 3.6).
- a new
The more complex defense-in-depth issues outlined in section 3.5 have been addressed in the open later on and are contained in release v1.3.4.
5) Disclosure Process
Once we established contact with the upstream author, we had a very constructive discussion of the coordinated disclosure process. Upstream quickly acknowledged the issues, opted for coordinated disclosure and communicated a time schedule when bugfixes were expected to be available for review and when a bugfix release of qSnapper would be published. When we agreed on the final bugfixes in the middle of May, we agreed on choosing an earlier publication date than originally intended.
We want to thank the upstream author for handling this report in a very professional fashion and for greatly improving the security and robustness of qSnapper.
6) Timeline
| 2026-04-09 | Lacking any other point of contact, we created a public GitHub issue asking for a security contact. |
| 2026-04-13 | The upstream developer responded in the issue providing an email address for us to reach out to. |
| 2026-04-13 | We reached out to the developer privately by email providing a detailed report and offering coordinated disclosure. |
| 2026-04-14 | Due to issues with mail servers our email did not reach the upstream developer. Upstream offered us another email address to try. |
| 2026-04-15 | We received a reply from the upstream developer confirming the issues and requesting coordinated disclosure. Upstream accepted our offer to assign CVEs for the issues. A preliminary disclosure date of 2026-07-07 was established. |
| 2026-04-17 | We assigned CVEs and shared them with upstream. |
| 2026-05-08 | We received a tarball containing the current release candidate code of qSnapper. |
| 2026-05-11 | We asked the upstream author if individual bugfixes could be supplied instead. |
| 2026-05-12 | We received the individual patches we asked for. |
| 2026-05-12 | We provided feedback on the current state of the patches. Apart from minor details and hardening suggestions the patches were already in good shape. |
| 2026-05-14 | We received updated patches for review and found no further issues. Given the good progress on the bugfixes, an earlier coordinated release date of 2026-05-26 was agreed upon. |
| 2026-05-26 | As planned, upstream released qSnapper 1.3.3 containing the bugfixes. |
| 2026-05-26 | Publication of this report. |
7) References
Change History
| 2026-06-26 | Updated section 4 with information about release v1.3.4 containing hardening bugfixes. |
MobileLinux Hackday #1 in České Budějovice Outperforms Prague!
Breaking New Ground: Mobile Linux Hackday #1 in České Budějovice Outperforms Prague! If you’ve been following the Mobile Linux journey in Czechia, you know we’ve built a fantastic routine in Prague. We have a really successful series behind us consisting of 7 monthly hackdays, always hosted at the Prague SUSE office. But when the stars […]
The post MobileLinux Hackday #1 in České Budějovice Outperforms Prague! appeared first on SUSE Communities.
openSUSE 16 の GNOME で Desktop icons NG(DING) を使う方法
GNOME には操作性等を拡張するための、種々の拡張機能が用意されています。このうち、Windows のように、デスクトップ上にファイルを直におけるようにする、Desktop icons NG(DING) は、GNOME 環境での操作性を大きく改善するため、よく使われている拡張機能です。
しかし、openSUSE 16 の GNOME に、この拡張機能をインストールしても、そのままでは動作しません。インストールはできますが、設定メニューが動かないのです。
調べてみたところ、/var/log/messages に
2026-05-25T10:11:38.899231+09:00 16gnm gnome-shell[5172]: Launching DING process
2026-05-25T10:11:39.088697+09:00 16gnm gnome-shell[5172]: DING: (gjs:12931): Gjs-CRITICAL **: 10:11:39.087: JS ERROR: Error: Requiring GLibUnix, version 2.0: Typelib file for namespace ‘GLibUnix’, version ‘2.0’ not found
というエラーが出ていました。そこで調べてみたところ、ものは
https://docs.gtk.org/glib-unix/unix.html
のようです。openSUSE の場合はどうやら typelib-1_0-GLibUnix-2_0 のようなので、これをインストールすると正常に動作するようになりました。
Soporte a largo plazo no significa lo que crees
Hoy quiero dar eco a una entrada bastante importante para entender como funciona el desarrollo de las distribuciones y por qué entender los conceptos es clave para hacer buenas elecciones. Bienvenidos a la entrada en la que Nate Graham (creador de los artículo de Esta Semana en Plasma) intenta explicar que soporte a largo plazo no significa lo que crees de una forma clara y sencilla. Algo que muchos ya sabemos pero que vale la pena recordar.
Soporte a largo plazo no significa lo que crees
De nuevo me hago eco de una entrada del blog Adventures in Linux and KDE de Nate Graham, en el que desgrana el significado real de «»Soporte a largo plazo» ( «Long Time Suport» o «LTS», en sus acepciones en inglés). Algo que nos pone sobre la mesa lo que es y lo que no es respecto a este concepto
Para empezar Nate nos quiere dejar claro que “Long-Term Support” no promete un sistema libre de fallos, sino una versión de software que recibe actualizaciones durante varios años, sobre todo parches de seguridad y, a veces, mantenimiento adicional.

Esto pinta bien: sistema robusto y a prueba de fallos, pero el mundo del Software es algo más complicado. Una cosa es el sistema pero otras son sus aplicaciones, que en este sistema suelen quedar fijadas a una versión concreta del software, sin nuevas funciones ni mejoras de interfaz durante su ciclo de vida. Los errores mayores serán solucionados pero los menores no. Las numerosas mejoras que lleguen para las aplicaciones no nos llegan a los LTS.
De esta forma la idea central es que una LTS es más bien una promesa de mantenimiento prolongado, no una garantía de estabilidad perfecta ni de soporte personal. Según subraya Nate, en una LTS pueden seguir existiendo bugs, crashes, problemas no corregidos y límites de compatibilidad con hardware nuevo, porque eso no forma parte de lo prometido .
Así que hay que tener claro si una LTS encaja con nuestro forma de utilizar nuestro sistema. Si quieres software más nuevo, mejores correcciones rápidas o mejor soporte de hardware suelen estar mejor en distribuciones de actualización rápida, mientras que una LTS favorece minimizar cambios e inconsistencias entre paquetes. No hay nada perfecto, si quieres estabilidad olvídate de novedades, si quieres novedades olvídate de estabilidad. Ambos conceptos están en los extremos de una balanza.
Nate también nos explica que existen las LTS gratuitas y la que vienen de la mano de un soporte comercial real. Según el artículo, si lo que se busca es una garantía fuerte de resolución de problemas y atención directa, eso ya entra en productos de pago como Ubuntu Pro, RHEL o SUSE con soporte empresarial . Si no es así, debes conformarte con una LTS comunitaria como Ubuntu LTS, Debian Stable o openSUSE Leap.

Para finalizar, Nate nos comenta que un buen complemento a las LTS en cuanto a tener aplicaciones a la última son los aplicaciopnes Flatpak o Snap, las cuales están actualizadas sin depender tanto del ritmo de la distro. Eso ayuda a tener software más nuevo, pero no elimina los inconvenientes de los formatos universales, como integración desigual, tamaño mayor o diferencias de comportamiento respecto a paquetes nativos.
Este último párrafo, junto uno de los comentarios que aparece en la entrada nos lleva a KDE Linux y lo que quiere conseguir: un sistema base pequeño y estable, compuesto por un cargador de arranque, el kernel, systemd y los controladores de dispositivos; mientras que todo el software de la interfaz gráfica se distribuiría entonces mediante la versión “flatpak-next” de Flatpak, que está en desarrollo y que, al parecer, resolverá todos los problemas que tenemos con la implementación actual.

¿La cuadratura del círculo? ¿Estabilidad y novedad en una misma distribución? Esperemos que si, el tiempo lo dirá.
La entrada Soporte a largo plazo no significa lo que crees se publicó primero en KDE Blog.

A Day With openSUSE at Polytechnics Mauritius
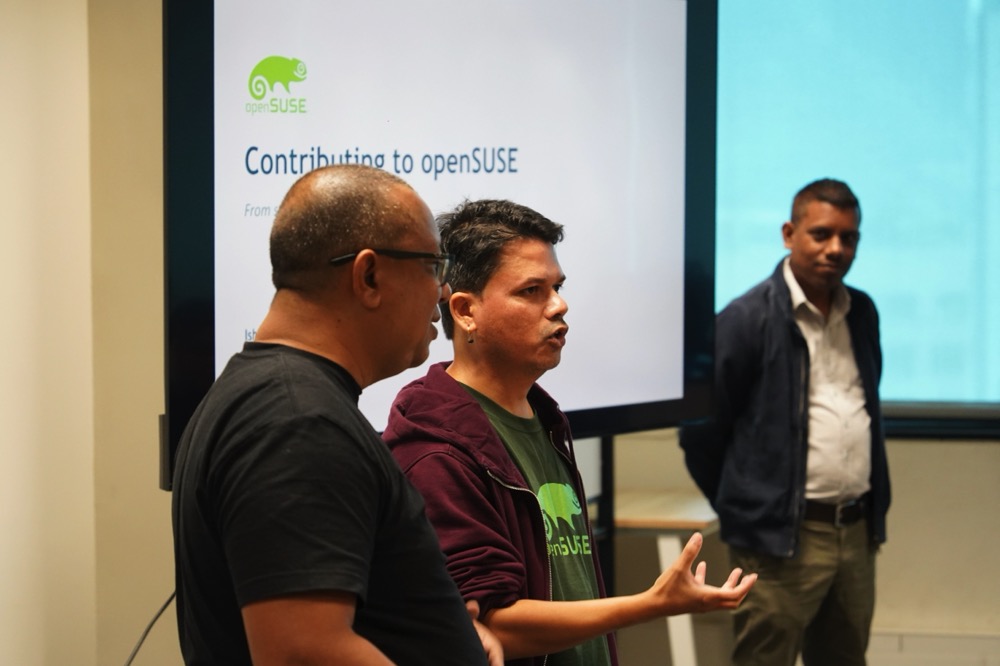
On Wednesday 13 May 2026, I spent the full day at the Polytechnics Mauritius campus in Ébène, running a workshop on open source software with openSUSE as the running thread. Morning and afternoon sessions, two distinct flavours, one community story. The day was organised and facilitated by Nishtee Gopee, Programme Leader of IT & Emerging Technologies at Polytechnics Mauritius, together with lecturers Arun Goorsaha and Salim Soobadar — who kept the energy in the room high and gently nudged every student to participate fully, ask questions, and stay for the demos. I was joined as co-presenter by two openSUSE friends from the local scene: Eddy Lareine and Neil Baichoo.
The Morning: How We Got Here
I opened with history, not commands. You cannot really appreciate why openSUSE looks and behaves the way it does without first understanding the soil it grew from.
So we went back to Richard M. Stallman, the GNU Project, and the four freedoms. Then to the BSD lawsuit that bogged the alternative UNIX world down for years, and to a Finnish student named Linus Torvalds who, while studying operating systems under Professor Andrew Tanenbaum and his teaching OS Minix, decided in 1991 to write his own kernel — "just a hobby, won't be big and professional like GNU."
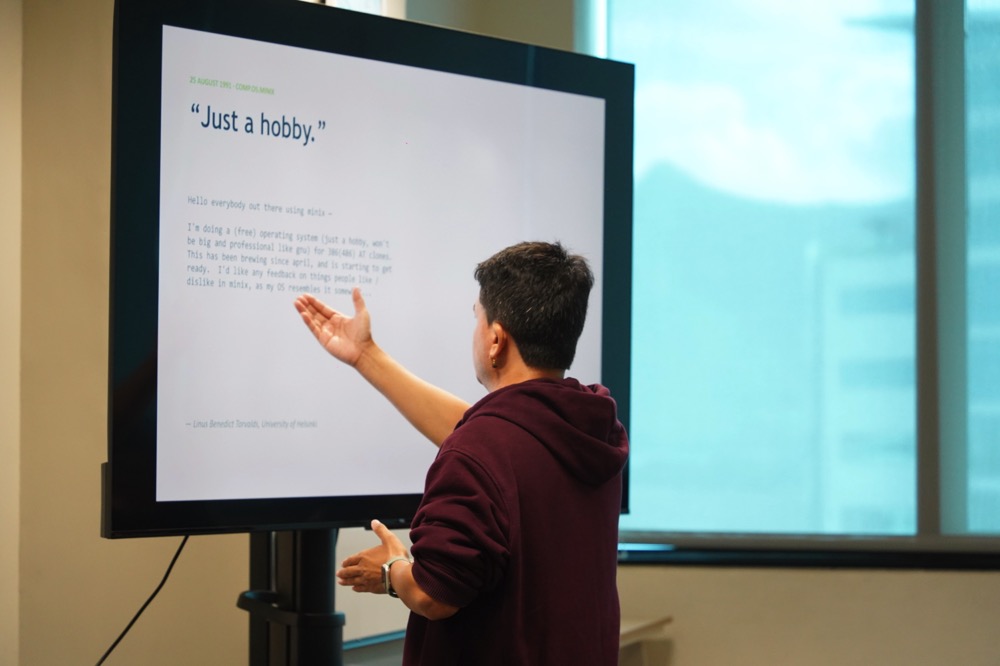
"Just a hobby." — The most consequential understatement in computing history.
From there it was a natural step into software licences — copyleft (GPL family), permissive (MIT, BSD, Apache), and the practical difference for someone who wants to use, modify, or ship code. We covered why the licence on a piece of code is not a detail you skim past, especially if you intend to build a product on top of it.
Then I shifted to openSUSE itself — thirty-four years on the same continent of Linux. Four German students starting S.u.S.E. in Nuremberg in 1992. YaST being born in 1994. Novell acquiring SUSE in 2003 for USD 210 million. The openSUSE.org project launching in 2005. EQT buying SUSE in 2018 for USD 2.5 billion. SUSE going public on the Frankfurt stock exchange in 2021. Going private again in 2023. And through all of that corporate motion, the openSUSE Project remaining independent, Board-elected, community-led.
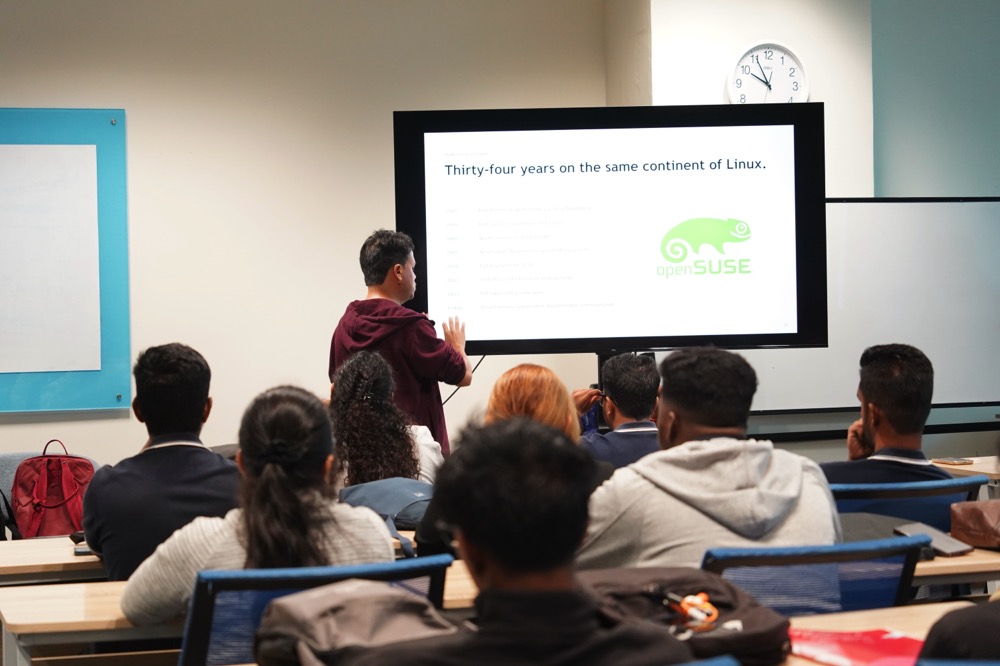
You Are Already Using Open Source
One slide I always enjoy showing is the "you are already using it" slide — the one that ends the imaginary debate about whether open source is mainstream. Android is Linux. Your iPhone has open source at its core. Netflix and Spotify run on it. TLS, OpenSSL and SSH guard every padlock icon you see. The Top500 supercomputers list is now 100 % Linux. Every meaningful AI model and framework — PyTorch, TensorFlow, JAX, vLLM — is open source. Firefox, GCC, LibreOffice, Inkscape, Blender. The audience went quiet for a moment. Good.
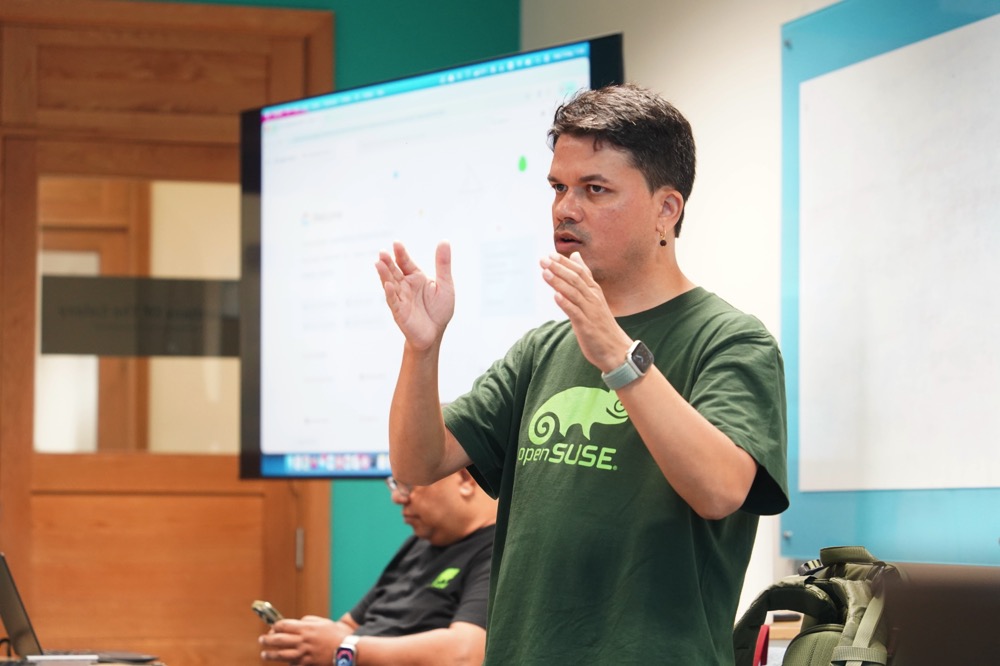
Contributing Without Writing Code
The biggest myth I wanted to dismantle that morning is the one that says you must be a kernel guru to contribute to open source. You don't. I walked the students through the non-coding tracks:
- Wiki and documentation — fixing typos, improving install guides, translating pages.
- Artwork and marketing — designing posters, social cards, release wallpapers.
- Advocacy — speaking at universities (like the one we were standing in), running booths at conferences, evangelising at meetups.
- Helping new users — answering questions on forums, on Matrix, on Discord, on the mailing lists. Mentoring someone through their first install is a contribution.
- Bug triage and testing — running pre-release images, filing reproducible bugs.
Most people who eventually become code contributors started on one of these tracks. That is worth saying out loud in a room of nineteen-year-olds who think the door is closed because they don't yet feel "technical enough".
Eddy on the openSUSE Board and Elections
Eddy Lareine then took the floor to talk about governance — the openSUSE Board, why the project has one, how elections are run, and why the rules around them matter. He explained the staggered mandate model: five board members, three-year terms, with a portion of the seats up for election each year. Continuity on one side, fresh ideas on the other. It's a design pattern I would actually borrow for any community of decent size.
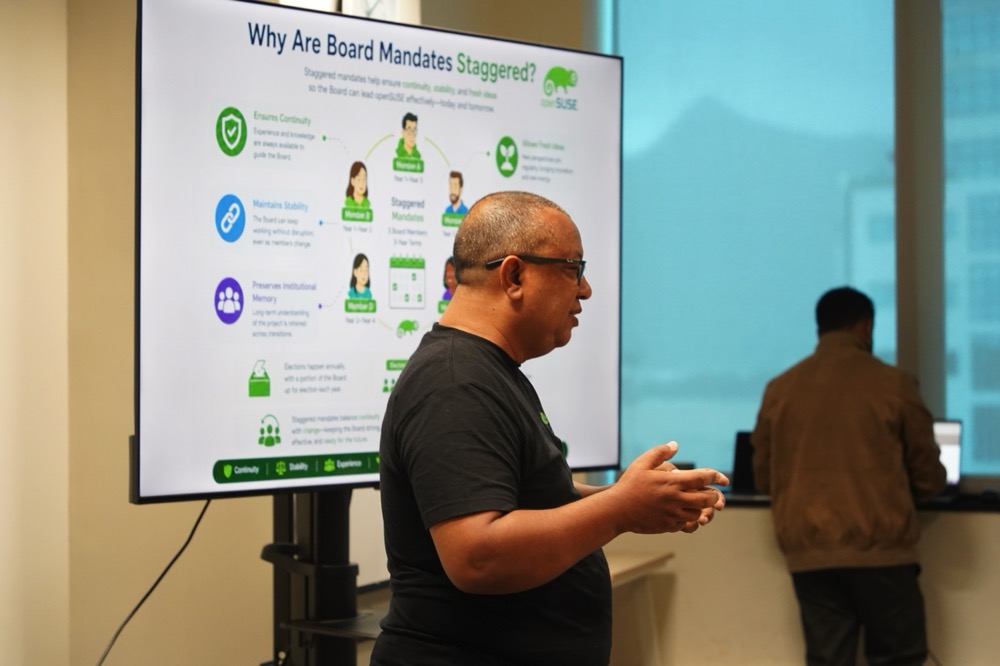
Eddy walking the students through how the openSUSE Board is structured.
For a room full of students who associate "open source" only with code on GitHub, seeing governance — election rules, voter eligibility, candidate manifestos — was a small revelation. Communities are not just code. They are agreements.
The Afternoon: Neil, KDE, and a Gecko on a Wallpaper
After lunch, Neil Baichoo presented. Neil is a software engineer who programmed in Rust for a specialised database company, and he is a long-time contributor to the KDE project. He opened with a broad look at open source as a whole — hitting a few well-known examples and pulling up their repositories on GitHub so the students could see code from the real world. Then he told his own contribution story in the openSUSE project.
Some time ago, Neil submitted a photograph he had taken of a Mauritius day ornate gecko — the bright green endemic species you see on coconut palms across the island. That photograph was selected and shipped as part of the default wallpaper set in openSUSE Leap 16.0 while the photo credit was attributed to Neil Baichoo.
The room lit up. The idea that a picture taken as a hobby could end up on Linux desktops worldwide was the most concrete demonstration of "your contribution matters" that any slide of mine could ever produce.
Neil also fielded the inevitable career question: "Should I learn Go or Rust to get a head start?" His honest answer — and I agree — was no. The global market for entry-level Go and Rust developers is small. In Mauritius, it is essentially zero. Learn the fundamentals well. Pick languages based on the problems you want to solve, not on hype cycles. Rust is wonderful when you have a reason to need it. PHP, Python, TypeScript, and Java will pay your bills.
The Open Build Service Demo
I then ran a live demo on how to package software for openSUSE using the Open Build Service (OBS). OBS is itself an open source project, maintained by the openSUSE community, used to build packages for openSUSE, SUSE Linux Enterprise, Debian, Ubuntu, Fedora, RHEL, Arch and others from a single spec.
The walkthrough covered:
- The OBS web UI at
build.opensuse.org— projects, packages, build results. - The
osccommand-line client — how to authenticate against your openSUSE account, check out a project, edit a.specfile, build locally withosc build, and submit withosc commit. - The anatomy of a
.specfile —Name,Version,Source0,BuildRequires,%prep,%build,%install,%files.
For the demo package, I picked FrankenPHP — partly because it isn't currently in the openSUSE repositories, and partly because it deserves to be. FrankenPHP is a modern, high-performance PHP application server built on top of the Caddy web server, officially supported by the PHP Foundation, and capable of dramatically speeding up Laravel and Symfony applications via its worker mode. Packaging it as a proper RPM means a one-line zypper install frankenphp for every openSUSE user.
I showed the build locally first, then a osc commit against my home project on OBS. Watching the dependency graph resolve and the package compile across multiple distributions and architectures, from a single spec file, is one of those "this is why I love openSUSE" moments.
openSUSE on Google Cloud, in Two Minutes
Several students wanted to know how to get started with openSUSE without re-partitioning their laptops. I switched tabs to the Google Cloud Console and walked them through spinning up a free-tier e2-micro Compute Engine VM with openSUSE Leap 16.0.
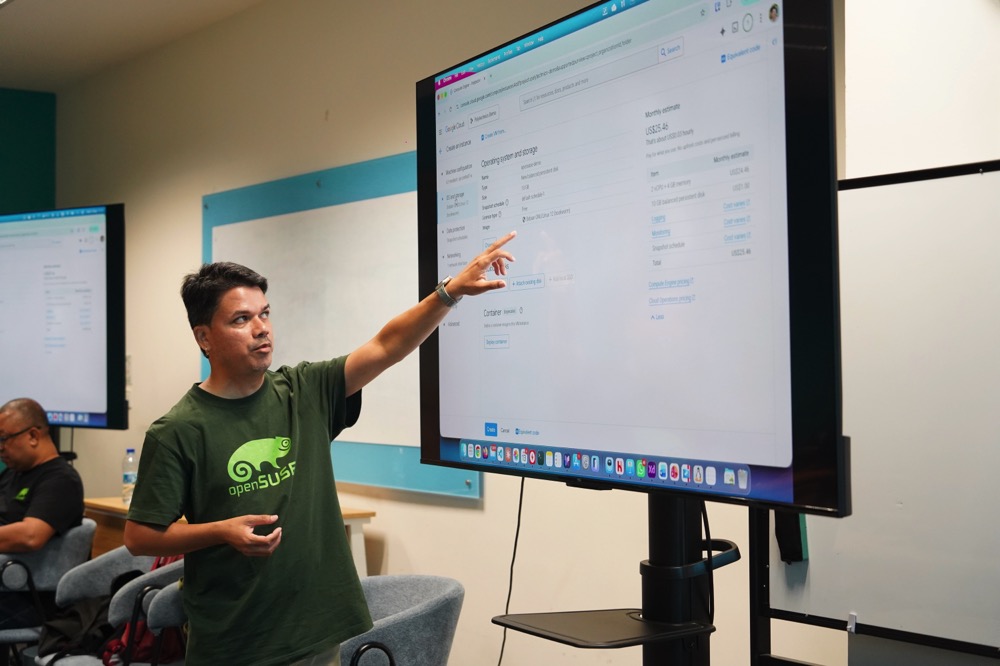
While at it, I clarified a question that comes up surprisingly often: the difference between SUSE Linux Enterprise Server (SLES) and openSUSE Leap on GCP.
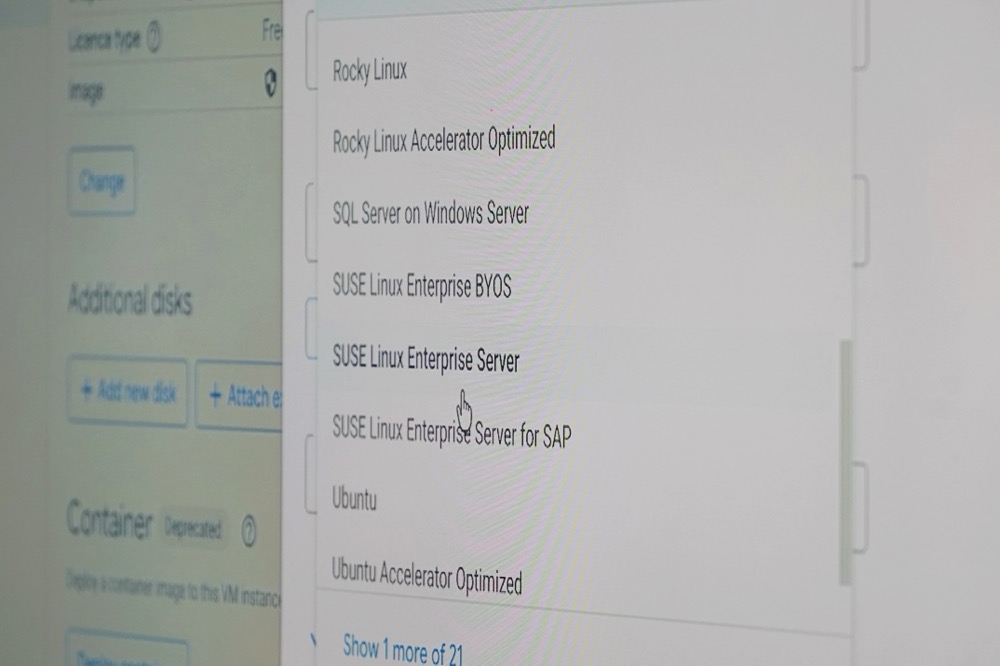
- SLES is the commercial product. The image carries a per-hour licence fee on top of the compute cost, and it ships with SUSA support entitlements. It is what you choose when you are running SAP HANA in production and you want a phone number to call at 3 a.m.
- openSUSE Leap is the community distribution, built from the same SLE codebase. The image is free of licence cost — you pay only for the compute and storage. It is what you choose to learn, to develop, to host your blog, or to build RPMs.
For a student on a free trial, openSUSE Leap on e2-micro in us-central1 (one of the free-tier regions) is the right starting point.
What Didn't Quite Go to Plan
Several students were keen to install openSUSE Leap 16.0 locally in VirtualBox. In theory: download the ISO, boot the VM, install. In practice, on a Wednesday at Polytechnics, three things went wrong:
- The campus Internet connection wasn't generous. Half the ISO downloads finished with corrupt images that failed checksum verification (or worse, booted into installer errors).
- Several laptops simply did not have enough free RAM or disk to give a VM a comfortable 4 GB / 20 GB allocation.
- The few that did succeed spent fifteen minutes in installer screens instead of actually using openSUSE.
This is the part of the day I will fix for next time.
Lessons Learned — A Browser-Based openSUSE Playground
The takeaway from the afternoon is clear: for a workshop setting, full local installation is the wrong shape of the problem.
What I want to build before the next session is a small web tool that drops a student straight into a fresh openSUSE Leap container running in their browser — a terminal in a <div>, a real shell on the other end, zypper working, osc pre-installed, no download, no ISO, no checksum failures, no VirtualBox.
Fast, fun, and productive. That's the shape of the next openSUSE workshop in Mauritius.
Closing Thoughts
A whole day workshop is a long time on your feet, but the energy in the room kept me going. Students who came in thinking "Linux is what servers run" left understanding that Linux is what everything runs — and that they have a seat at the table from day one, whether they write code, write documentation, take photographs of geckos, or simply show up to help someone else install their first distro.
A big thanks to Polytechnics Mauritius for hosting us at the Ébène campus, to Nishtee Gopee, Arun Goorsaha and Salim Soobadar for organising the day and bringing such an engaged cohort into the room, to Eddy and Neil for joining as co-presenters, and to every student who stayed past 4 p.m. to ask "one more question" at the front of the room.
Lanzado Haruna 1.8, nueva versión de este reproductor multimedia de KDE
El mundo de las aplicaciones de la Comunidad KDE es casi infinito. Hace cuatro años que presenté Haruna, otro reproductor multimedia que se une a las alternativas KDE como Dragon Player o Kaffeine y que sigue su desarrollo. Por eso me complace compartir con vosotros que ha sido lanzado Haruna 1.8, que llega cargado de novedades.
Lanzado Haruna 1.8, nueva versión de este reproductor multimedia de KDE
Siempre es de agradecer tener varias opciones para cualquier funcionalidad básica de nuestro sistema, y en eso el Software Libre es sobresaliente, y es que en ocasiones podemos tener problemas con uno de ellos o que simplemente nos guste uno más que otro.
Tenemos a nuestra disposición decenas de reproductores multimedia como VLC o SMPlayer, y la Comunidad KDE te ofrece incluso un par dentro de su ecosistema, los ya nombrados Dragon Player o Kaffeine.

A este elenco se unió hace años Haruna, un reproductor de vídeo de código abierto construido con libmpv que destaca por su integración con Youtube y que sigue evolucionando a su ritmo dado que hace poco ha llegado a su versión 1.8.
Entre sus novedades destacan:
- Posibilidad de abrir múltiples archivos desde la línea de comandos y no todos los de la carpeta.
- Acción de detener,disponible en la reproducción.
- Añadido ajuste para activar el progreso en la barra de tareas.
- Mostrar el nombre del archivo/título en el OSD (visualización en pantalla) al abrir un archivo.
- MPRIS: buscar y establecer la portada desde un archivo de imagen externo para archivos de audio sin portadas internas.
- Animación de carga personalizada.
- Ajuste para la propiedad sub-border-style de mpv.
Respecto a la Lista de reproducción también tenemos nuevas funcionalidades
- Elemento de menú para abrir el archivo en la aplicación MediaInfo ( si está instalada).
- Permitir la ordenación ascendente/descendente para la opción «Ninguna» (None).
- Indicador de la posición de reanudación de la reproducción debajo de la duración.
- El tirador para arrastrar elementos ahora se muestra al pasar el cursor por encima (hover).
Haruna, otro reproductor multimedia de KDE
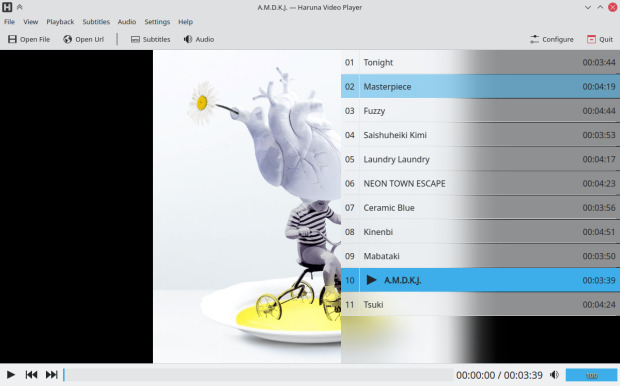
Las principales características de Haruna son las siguientes:
- Posibilidad de poner una lista de reproducción automática.
- Atajos de teclado configurables.
- Reproducción de vídeos en línea a través de youtube-dl/yt-dlp
- Saltar automáticamente los capítulos que contengan determinadas palabras
- Asignación de acciones a los botones del ratón: clics simples y dobles a la izquierda, al centro y a la derecha, así como desplazamiento hacia arriba y hacia abajo
- Salto rápido al siguiente capítulo haciendo clic en el centro de la barra de progreso.
- Posibilidad de cambiar los esquemas de color así como los estilos de los widgets/controles.
Más información; Haruna
La entrada Lanzado Haruna 1.8, nueva versión de este reproductor multimedia de KDE se publicó primero en KDE Blog.